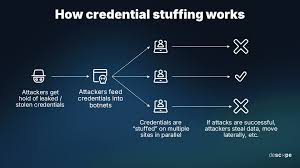
A recent report from Kaspersky has revealed that half of the compromised passwords in 2025 were already leaked in previous data breaches. The study highlights ongoing concerns about password safety, as many users continue to use weak passwords that are easy to guess. It found that common patterns, like using predictable elements such as birthdays or simple sequences, make passwords vulnerable to attacks.

Kaspersky’s research also showed that many leaked passwords have not been changed for several years, with the average lifespan of a compromised password being about 3.5 to 4 years. This reuse of old passwords raises significant security risks as cybercriminals take advantage of this tendency. The report advocates for stronger security measures, urging users to adopt more secure methods of authentication, such as passkeys, which provide better protection against threats like phishing.
With cyberattacks on the rise, Kaspersky emphasizes the need for organizations and individuals to prioritize better password management practices. By recognizing the vulnerabilities in current systems, Kaspersky aims to encourage a shift toward more robust security solutions that safeguard personal data more effectively.
About the Author