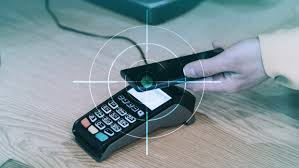
Cybersecurity firm Kaspersky has reported a staggering 188% surge in NFC relay attacks targeting smartphone users in 2026. NFC, or Near Field Communication, is the technology that allows you to tap your phone to pay for goods or transfer data. In a relay attack, criminals use two devices to intercept and extend the wireless signal from your phone without your knowledge. This means a thief standing several meters away – or even on the other side of a wall – can trick a payment terminal into thinking your phone is right next to it, draining money from your linked card or wallet app.

The report explains that these attacks typically happen in crowded public spaces such as train stations, shopping malls, and airports. One criminal stands near the victim with a device that captures the NFC signal from their phone, while an accomplice stands near a payment terminal with another device that replays that signal. The two devices communicate over the internet or Bluetooth, effectively “relaying” the signal over long distances. Victims often do not realize anything is wrong because their phone never leaves their pocket or bag, yet unauthorized payments are deducted instantly. Kaspersky noted that Android phones are currently more vulnerable due to certain default settings, but iPhones are not completely immune.
To protect against these attacks, Kaspersky advises users to turn off NFC when not in use, avoid carrying contactless cards or enabled phones in crowded areas, and use RFID-blocking wallets or phone cases. The company also recommends setting up payment authentication such as fingerprint, face ID, or a PIN for every transaction instead of allowing small payments to go through without verification. Banks and mobile payment providers are being urged to introduce better encryption and distance-checking features. As tap-to-pay continues to grow in Nigeria and globally, experts say users must stay alert to this silent but fast-growing threat.
About the Author