Security firm Kaspersky has uncovered a new phishing method that uses Bubble, a popular no‑code platform, to bypass normal security filters. Attackers build lightweight web apps on Bubble’s trusted *.bubble.io domains and use them as hidden redirectors. Because these intermediary apps sit on legitimate infrastructure, they look more credible and are less likely to be blocked by automated defences.

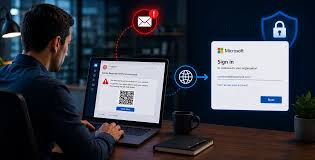
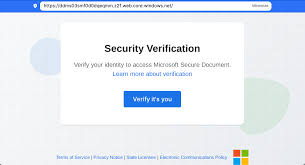
In the campaign Kaspersky observed, victims were forwarded from the Bubble app to a convincing fake Microsoft login page, with an extra Cloudflare verification step to hide the attack. Criminals are also combining this tactic with ready‑made phishing kits and phishing‑as‑a‑service offerings that can intercept session cookies, perform AiTM (adversary‑in‑the‑middle) attacks, and even generate phishing emails using AI. These toolsets often include geo‑filters and anti‑detection features and are hosted on reputable cloud services to avoid blacklisting.
Kaspersky warns that using legitimate development platforms this way makes it harder for both users and security systems to tell real sites from malicious ones. The firm says the trend raises the risk of credential theft, unauthorised access and data breaches, and urges organisations and users to tighten email and web filtering, enable multi‑factor authentication, and treat unexpected verification prompts or login requests with suspicion.
About the Author